
Key Takeaways
01
Agentic AI is designed to pursue goals, not simply generate responses.
02
The best opportunities are usually multi-step business workflows with measurable outcomes.
03
Production agents require more than an LLM: they need tools, data, orchestration, memory/state, permissions, evaluation and observability.
04
RAG improves access to information; agentic systems add planning and action around that information.
05
More autonomy creates more operational risk, which means permissions, approval gates and auditability must be architectural concerns.
06
Multi-agent systems should be introduced only when the workflow genuinely benefits from specialised agents.
07
AI agent ROI should be measured through business outcomes such as cycle time, resolution rate, conversion, cost-to-serve and error reduction—not token usage alone.
08
A practical implementation normally starts with a bounded workflow, proves reliability and then expands the agent's authority.
AI has moved from answering questions to helping businesses get work done. Generative AI made it easy to create text, code, summaries and recommendations. Agentic AI takes the next step: it can work toward a goal, decide what needs to happen next, use software tools, inspect results and continue within defined rules.
That sounds simple until you try to put an agent into a real business process. A customer-service agent may need customer data, order history, policies, a ticketing system and permission to take specific actions. A finance agent may need ERP access, approval rules and an audit trail. A coding agent needs a repository, test environment and controlled deployment path.
That is why agentic AI is not just an LLM with a prompt. It is a software architecture for goal-oriented work. IBM describes agentic AI as systems that can plan and perform tasks with a degree of autonomy, typically combining foundation models with tools, data and traditional software controls.
The business question is therefore bigger than “Which model should we use?”
Which workflow should the agent improve, what authority should it have, and how will we prove that it is working safely?
This guide explains what agentic AI means in practical terms, how AI agents work, where they create measurable business value, what a production architecture looks like, what AI agent development can cost, and how to implement autonomy without turning a promising pilot into an uncontrolled system.
Planning an AI agent but unsure where to start?
Map the workflow, systems, data, risk, and success metric before choosing a model or framework.
→ Talk to Designoweb's AI team
01
What Is Agentic AI?
Agentic AI refers to AI systems designed to pursue objectives through a sequence of decisions and actions with limited human intervention.
A useful mental model is:
Goal → Context → Reasoning → Tool selection → Action → Observation → Evaluation → Next action
The system may repeat that loop several times before completing the task.
This is materially different from a simple prompt-response application.
02
Agentic AI vs a traditional AI application
| Capability | Traditional AI / GenAI application | Agentic AI |
|---|---|---|
| Receives a prompt | yes | Yes |
| Generates content | Yes | Usually |
| Retrieves information | Sometimes | Usually |
| Makes a plan | Limited | Core capability |
| Selects tools dynamically | Limited | Common |
| Executes actions | Usually through predetermined workflows | Core capability |
| Responds to changing conditions | Limited | Designed for it |
| Maintains task state | Sometimes | Usually |
| Works across multiple systems | Possible | Common |
| Human approval | Optional | Often part of risk design |
| Continuous evaluation | Recommended | Essential |
The important point is that not every AI workflow needs to be agentic.
A classification model predicting customer churn does not automatically need an agent.
A knowledge assistant answering questions from company documents does not automatically need an agent.
An automated invoice workflow that must inspect an invoice, validate vendor information, check purchase-order status, resolve discrepancies and route exceptions may benefit substantially from agentic behaviour.
Agentic AI Market & Adoption Snapshot
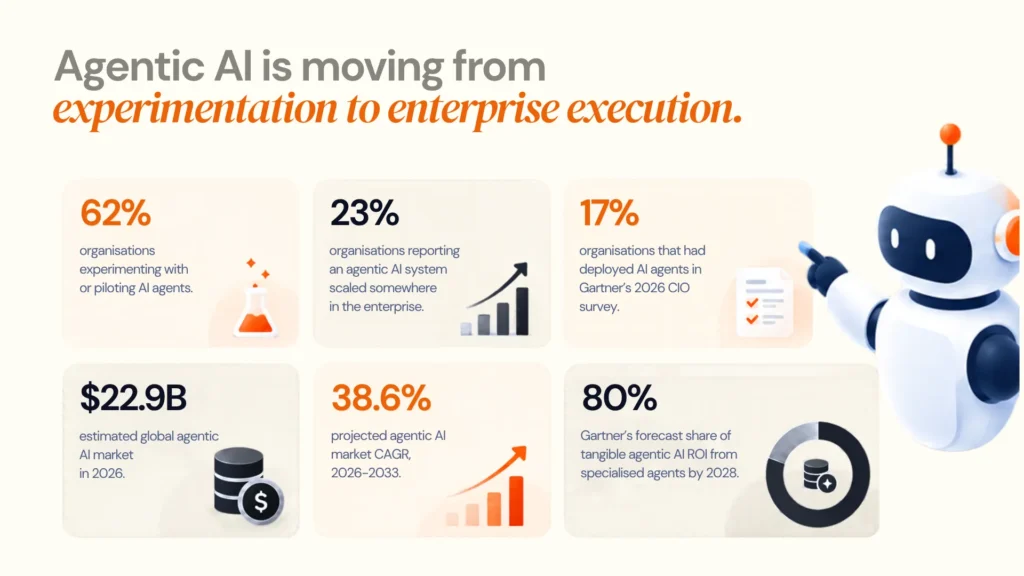
Agentic AI has moved quickly from a research topic into enterprise experimentation, but the gap between trying agents and scaling them is still significant. That distinction is important for business leaders because market growth does not automatically translate into production value.
McKinsey reported in April 2026 that 62% of organisations were experimenting with or piloting AI agents, while only 23% had scaled an agentic AI system somewhere in the enterprise. The same research found that, in any given business function, no more than 10% of respondents said their organisations were scaling AI agents.
Gartner's 2026 research offers another view: 17% of organisations had deployed AI agents, while more than 60% expected to do so within the following two years. Gartner's analysis of 107 agentic AI deployments also predicts that, by 2028, 80% of tangible ROI from agentic AI will come from specialised, domain-specific agents rather than broad general-purpose agents.
The commercial market is expanding as well. Grand View Research estimates the global agentic AI market at $22.9 billion in 2026, with a projection of $224.5 billion by 2033 at a 38.6% CAGR. This is a market forecast—not a prediction of what an individual business will spend or earn.
What these numbers mean for technology leaders
The opportunity is real, but the useful question is not simply how quickly the market is growing. It is whether your organisation has a workflow, data foundation, integration layer, governance model, and success metric that can support an agent in production.
The pattern is clear: experimentation is scaling faster than reliable enterprise execution.
Agentic AI Numbers
62%
organisations experimenting with or piloting AI agents
23%
organisations reporting an agentic AI system scaled somewhere in the enterprise
17%
organisations that had deployed AI agents in Gartner's 2026 CIO survey
$22.9B
estimated global agentic AI market in 2026
38.6%
projected agentic AI market CAGR, 2026–2033
80%
Gartner's forecast share of tangible agentic AI ROI from specialised agents by 2028
Source line: McKinsey, Gartner and Grand View Research
The growth story is strong. Production reliability is the real engineering challenge.
03
Types of AI Agents
Not every AI agent needs the same level of autonomy. For most businesses, the useful distinction is the workflow an agent is responsible for and how much authority it has, not a long list of theoretical agent categories.
| Agent type | What it does | Example |
|---|---|---|
| AI copilot | Assists a human with analysis or execution | Drafting a sales follow-up |
| Workflow agent | Completes a bounded multi-step process | Resolve an eligible delivery exception |
| Research agent | Searches, compares and synthesises information | Prepares a competitor brief |
| Coding agent | Inspects, changes and tests software | Fixes a repository issue and prepares a pull request |
| Operations agent | Monitors conditions and coordinates actions | Detects a supply-chain disruption and routes the response |
| Multi-agent system | Coordinates multiple specialised agents | Research + analysis + approval workflow |
Which type should a business choose?
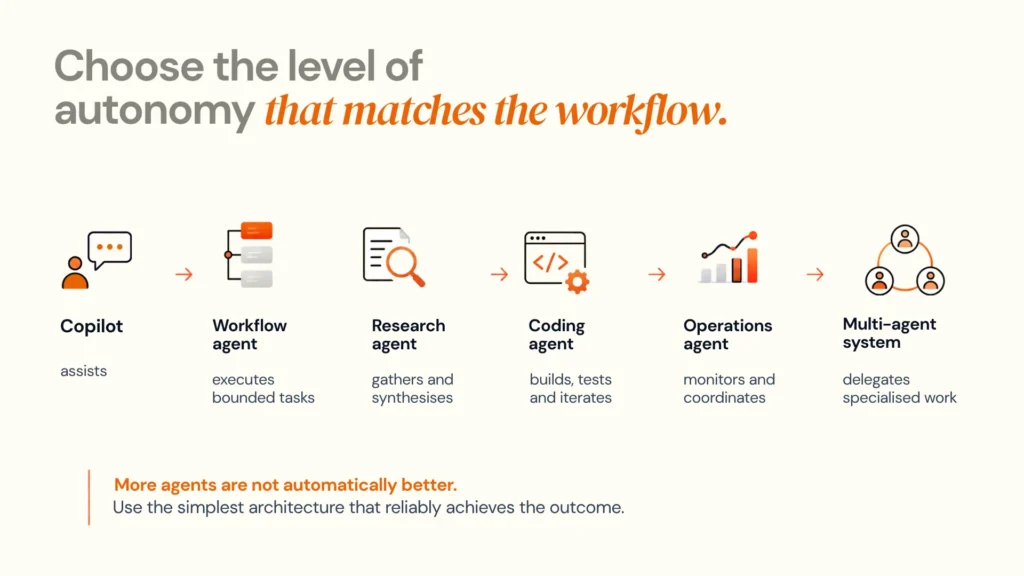
Start with the smallest unit of autonomy that can solve the workflow. A copilot may be enough when a person remains responsible for every action. A workflow agent becomes more relevant when the process contains repeatable decisions and tool calls. A multi-agent system should be reserved for workflows where distinct responsibilities genuinely benefit from specialised agents and orchestration.
04
How Agentic AI Works
A production agent is better understood as a software system than as a single model.
At minimum, the system usually combines an LLM or other reasoning model with context, instructions, tools, and an execution loop.
1. Goal and instructions
The agent receives an objective and operating constraints.
For example:
Resolve eligible customer delivery complaints while following the company's refund policy.
The objective is paired with instructions defining what the agent may and may not do.
This is where prompt engineering becomes more than writing a clever prompt.
The system needs explicit definitions for:
- task objectives
- permitted tools
- prohibited actions
- escalation conditions
- required information
- response formats
- termination conditions
2. Context and knowledge
The agent needs access to the information required to make decisions.
This might come from:
- CRM records
- ERP systems
- product databases
- knowledge bases
- documents
- APIs
- databases
- business rules
- previous interactions
Retrieval-augmented generation, or RAG, can provide relevant enterprise information at runtime rather than relying on information encoded in a model's training data.
For more interconnected information, architectures can combine semantic retrieval with knowledge graphs or GraphRAG. Google Cloud's current architecture guidance describes agentic systems that combine vector search and knowledge graphs to retrieve context from complex, multimodal data environments.
3. Reasoning and planning
The reasoning model determines the next step.
For a support workflow, the agent could reason:
- Identify the customer.
- Retrieve the order.
- Check shipment status.
- Determine whether the delay breaches policy.
- Select an eligible resolution.
- Ask for approval when the resolution exceeds its authority.
- Update the CRM.
- Notify the customer.
Not every implementation should expose or rely on unrestricted chain-of-thought. What the production system needs is observable decision behaviour, structured outputs and verifiable actions.
4. Tool use
Tools give an agent the ability to interact with the rest of the technology environment.
Examples include:
get_customer()
get_order()
search_inventory()
create_ticket()
send_email()
create_invoice()
schedule_meeting()
run_report()
Tools should be explicit, scoped, and permission-controlled.
This is one of the reasons agentic applications increasingly resemble distributed software systems rather than isolated AI features.
Current agent infrastructure is also evolving quickly. For example, OpenAI introduced its Agents API in September 2026 to support long-running agents, tool use, context management, orchestration, and subagents.
5. Observation and feedback
After an action, the agent needs to inspect what happened.
A tool call may:
- succeed
- fail
- return incomplete information
- return a contradictory result
- trigger a permission error
- produce a result that violates a business rule
A production agent needs a mechanism to decide what happens next.
That could mean:
retry → alternative tool → ask a human → stop → compensate → escalate
This feedback loop is one of the characteristics that separates an agentic system from a static LLM integration.
6. State and memory
Agents often need state during a task and, in some applications, across tasks.
It helps to distinguish:
Short-term state: what the agent needs to finish the current workflow.
Long-term memory: information retained for future interactions.
Memory should not be treated as an unrestricted database of everything the agent has seen.
Retention rules, access control, deletion policies, and data minimisation remain important, particularly when personal or confidential information is involved.
05
Agentic AI vs Generative AI vs RPA
These technologies overlap, but they should not be treated as interchangeable.
| Approach | Core behaviour | Best suited to | Main limitation |
|---|---|---|---|
| Traditional automation | Executes predefined instructions | Stable, deterministic workflows | Breaks when conditions change |
| RPA | Automates interaction with software interfaces | Repetitive structured tasks | Often fragile when interfaces or rules change |
| Generative AI | Generates or transforms information | Content, analysis, summarisation, assistance | Usually stops after producing an output |
| AI copilot | Assists a human during work | Knowledge work and decision support | Human remains responsible for execution |
| AI agent | Plans and executes multi-step work | Variable workflows involving tools and decisions | Requires stronger governance and evaluation |
| Multi-agent system | Coordinates specialised agents | Complex workflows with separable roles | More coordination, cost and failure points |
The critical distinction
A useful way to think about the progression is:
Automation follows instructions.
Generative AI produces an output.
An agent determines the next action within constraints.
That does not make agents universally superior.
A deterministic workflow is often preferable when the sequence is fixed, the rules are clear and the cost of variation is high.
Agentic behaviour becomes more interesting when the environment is dynamic.
Where Agentic AI Creates Business Value
The strongest business cases tend to share five characteristics:
- The workflow occurs frequently.
- It requires multiple steps.
- Inputs vary.
- Several systems or tools are involved.
- Success can be measured.
Business Benefits of Agentic AI
When the workflow is well chosen, agentic AI can create value across a few recurring dimensions:
- Faster cycle times: fewer manual handoffs between systems and teams.
- Lower cost-to-serve: more routine work handled without adding the same amount of headcount.
- Higher operational capacity: employees spend less time searching, copying data or coordinating routine tasks.
- Better exception handling: agents can gather context across systems before escalating an issue.
- More consistent execution: repeatable policies can be embedded into tool permissions, workflows, and approval rules.
These are potential outcomes, not automatic benefits. The business case still depends on data quality, process design, integration effort, and how reliably the agent performs.
Customer service and operations
Agentic customer-service workflows can coordinate:
- customer identity
- account information
- order information
- support history
- product knowledge
- fulfilment systems
- refund policies
- ticketing systems
- communications
The right boundary is usually not “let the agent solve everything.”
Instead:
Automate low-risk, repeatable decisions. Escalate exceptions.
For example, an agent might independently close a duplicate support ticket but require human approval for a large compensation request.
Sales and revenue operations
Agents can support workflows such as:
- account research
- lead qualification
- CRM enrichment
- meeting preparation
- follow-up
- opportunity summaries
- proposal preparation
- next-best-action recommendations
The value comes from reducing the gap between information and execution.
An agent that identifies a high-intent prospect but cannot update the CRM or trigger a follow-up workflow is still useful.
But the system becomes substantially more operational when the required actions are connected through governed tools.
Finance and back-office operations
Agentic systems can support workflows such as:
- invoice classification
- purchase-order matching
- exception identification
- expense review
- payment preparation
- reconciliation support
- financial reporting workflows
The risk level changes considerably once money can move.
A useful architecture might allow the agent to:
read financial data → analyse → prepare transaction → request approval → execute
rather than:
read financial data → independently transfer money
The architecture should reflect the consequences of failure.
Supply chain and logistics
Supply chains are particularly interesting because conditions change constantly.
An agent could monitor:
- inventory
- demand
- supplier status
- shipment exceptions
- weather or transport information
- warehouse conditions
- delivery schedules
It could then propose or execute actions based on predefined authority.
Nagarro's transportation agentic AI example illustrates the difference between a system that merely analyses a disruption and one that can coordinate context, formulate an operational response and trigger actions through connected tools.
Software engineering
Software development is already becoming one of the most visible agentic workflows.
Agents can assist with:
- repository analysis
- issue interpretation
- code generation
- test creation
- test execution
- debugging
- pull-request preparation
- documentation
- deployment workflows
The important change is the feedback loop.
A code-generation model produces code.
A development agent can:
inspect repository → modify files → run tests → interpret failures → revise → rerun → prepare change
AWS describes this model as an architecture where an agent can write, test, deploy and refine code through rapid feedback cycles.
For businesses, that creates an important engineering question:Where should AI be allowed to modify production systems, and where should human review remain mandatory?
Research and knowledge work
Research agents can:
- gather information
- search internal and external sources
- compare evidence
- extract findings
- create structured outputs
- monitor changing information
- notify teams when a condition changes
This is valuable when a task involves information retrieval plus synthesis plus follow-up actions.
It is less valuable when the task is simply:
“Summarise this document.”
A conventional LLM workflow may be enough.
Healthcare and other high-stakes domains
Healthcare creates an important distinction between automating administrative workflows and automating high-impact decisions.
Potential use cases include:
- administrative coordination
- patient communication
- document processing
- appointment workflows
- information retrieval
- operational triage support
Higher-risk clinical decisions require substantially stronger controls, domain validation and regulatory assessment.
The lesson generalises:
The higher the consequence of an incorrect action, the more carefully autonomy should be constrained.
06
Agentic AI Architecture for Production
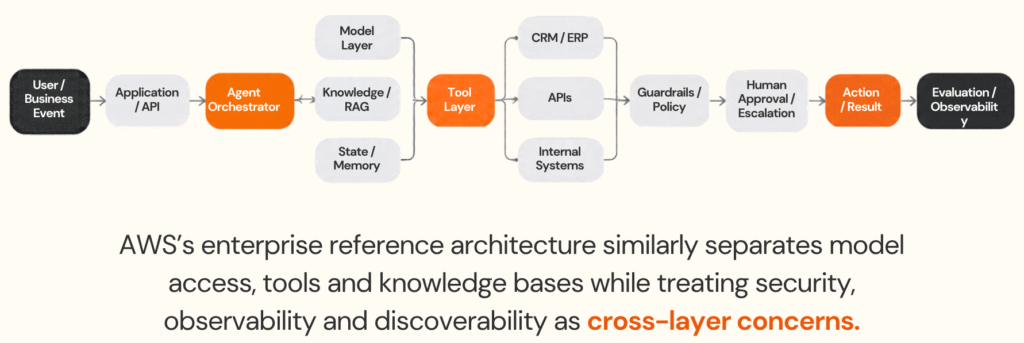
Production architecture is where many agentic AI discussions become too simplistic.
An agent is not just:
LLM + prompt + tool
A useful production architecture looks more like this:
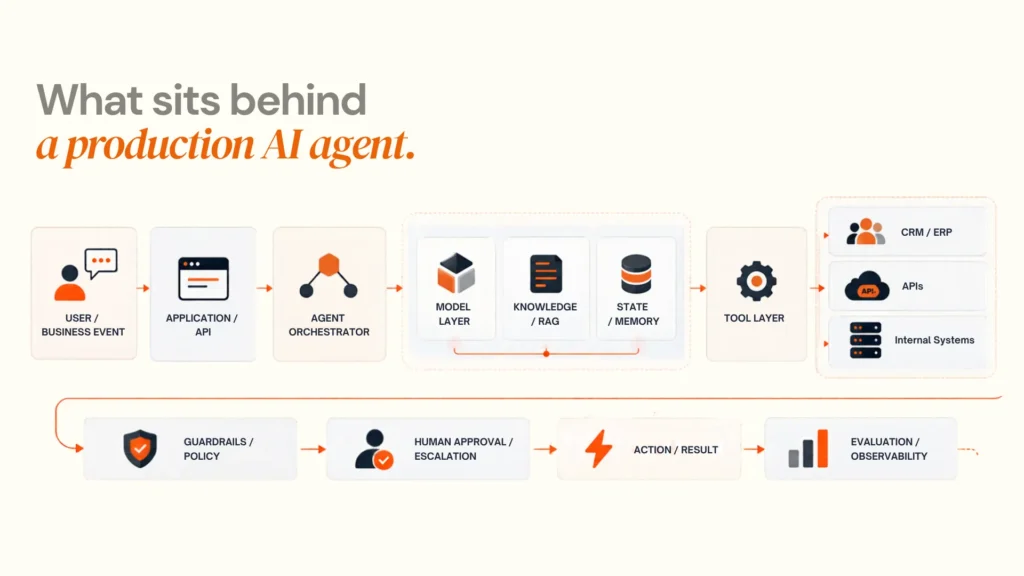
AWS's enterprise reference architecture similarly separates model access, tools and knowledge bases while treating security, observability and discoverability as cross-layer concerns.
Model layer
The LLM is responsible for language understanding, reasoning and planning.
But model selection should follow the workflow rather than define it.
A useful decision considers:
- reasoning quality
- latency
- context requirements
- structured-output reliability
- tool-use performance
- cost
- privacy requirements
- hosting requirements
- vendor dependencies
A more expensive model is not automatically the better business decision.
Some agent steps may need advanced reasoning.
Others may be better handled by smaller, faster models or deterministic code.
Orchestration layer
The orchestrator determines:
- which agent or workflow runs
- which tools are available
- how state is managed
- when retries occur
- when execution stops
- when a human is involved
Orchestration can be code-driven, graph-based, framework-based or managed through a platform.
The architecture should follow the workflow.
Do not introduce a framework merely because it is fashionable.
Knowledge and RAG layer
RAG provides external context to the reasoning system.
A typical RAG workflow looks like:
query → embedding → retrieval → context assembly → model response
An agentic workflow may look like:
goal → decide whether retrieval is needed → retrieve → reason → choose tool → act → inspect result → continue
That distinction matters.
RAG answers:
“What information should the model see?”
Agentic orchestration answers:
“What should the system do next?”
Tool layer
Tools should be treated as governed software interfaces.
Good tool design includes:
- narrow responsibilities
- typed inputs
- structured outputs
- explicit permissions
- predictable errors
- idempotency where relevant
- logging
- versioning
A single update_customer_account() tool is easier to govern than an unrestricted database connection.
MCP and tool interoperability
Model Context Protocol has become part of the rapidly evolving agent infrastructure landscape. The July 2026 MCP specification introduced a stateless protocol core alongside updated SDKs, authorization hardening and other changes aimed at scaling agent workflows. MCP 2026 specification
For businesses, the important point is not adopting MCP simply because it is popular.
The important question is whether a standardised tool interface makes the agent ecosystem easier to:
- integrate
- secure
- observe
- replace
- scale
State and memory
State should be designed rather than left to emerge.
You need to determine:
- what information exists only for the current task
- what should persist
- who can access it
- how long it is retained
- how it can be corrected
- how it can be deleted
Guardrails
Guardrails can operate at multiple levels:
Input controls: What requests are accepted?
Model controls: Which content and behaviours are allowed?
Tool controls: Which actions are available?
Data controls: Which data can be retrieved?
Action controls: Which outcomes require approval?
Output controls: What can be communicated externally?
The strongest systems do not rely on one guardrail.
They create multiple control layers.
Observability
Agent observability must track more than application uptime.
Useful signals include:
- model calls
- tool calls
- execution path
- retries
- failed actions
- escalation events
- latency
- token usage
- cost
- policy violations
- task completion
- human intervention
AWS describes AgentOps as an operational discipline aimed at the unpredictable decisions, costs and debugging challenges that arise when agents move into production. AWS AgentOps guidance
07
How to Decide Which Processes Should Become Agentic
The most valuable agent may not be the most complex one. A practical way to evaluate a candidate workflow is to score it against six dimensions.
| Criterion | Low opportunity | High opportunity |
|---|---|---|
| Frequency | Rare | Daily / continuous |
| Number of steps | 1–2 | Many |
| Variability | Predictable | Variable |
| Systems involved | One | Multiple |
| Human effort | Minimal | Significant |
| Outcome measurement | Difficult | Clear |
A simple Agentic Fit Framework
Ask:
1. Does the workflow have a defined outcome?
“Make customer service better” is too vague.
“Resolve eligible delivery exceptions within 10 minutes” is measurable.
2. Does the workflow require judgement between steps?
If every step is fixed, conventional automation may be better.
3. Does the system have the information and tools it needs?
An agent cannot reliably execute a workflow if key information remains trapped in disconnected systems.
4. Can mistakes be contained?
An agent updating a draft record is different from an agent approving a multimillion-dollar transaction.
5. Can success be measured?
Define the KPI before building the agent.
6. Does autonomy create enough value to justify its complexity?
This last question is frequently skipped.
A process can technically support agentic AI and still be a poor candidate.
Decision matrix
Decision matrix
Workflow characteristic
- Fixed sequence + deterministic rules
- Content generation
- Knowledge retrieval
- Human makes final decision
- Variable multi-step work
- Multiple specialised reasoning roles
- High consequence + low tolerance for error
Recommended approach
- Traditional automation
- Generative AI
- RAG / AI assistant
- Copilot / decision support
- AI agent
- Multi-agent system
- Bounded automation + human approval
08
Building and Implementing AI Agents
A production implementation should generally follow a staged approach.
Phase 1: Define the business outcome
Start with the workflow, not the technology.
Define:
- trigger
- user
- objective
- inputs
- systems involved
- expected output
- actions
- exceptions
- approval requirements
- success metrics
For example:
“Reduce manual handling of Tier-1 order exceptions by 50% while maintaining a human approval threshold for financial compensation above £X.”
This is substantially more useful than:
“Build an AI agent for customer service.”
Phase 2: Map the workflow
Document the current process.
Identify:
- repetitive steps
- decisions
- handoffs
- bottlenecks
- data dependencies
- systems used
- failure points
This is where existing process-engineering expertise matters as much as AI expertise.
Designoweb's end-to-end product development approach spans strategy, discovery, design, architecture, development, QA, deployment and ongoing improvement. Businesses considering an agent should use that broader engineering lens rather than treating the AI layer as a standalone feature.
Phase 3: Choose the simplest viable architecture
Do not begin with a multi-agent system because the workflow sounds sophisticated.
Start with:
Deterministic workflow → add LLM where uncertainty exists → add tool use → add agentic planning only where it creates value
This often produces a more maintainable system than starting with maximum autonomy.
Phase 4: Build the tool layer
Define the agent's capabilities.
Each tool should have:
- clear purpose
- controlled permissions
- validation
- error handling
- observability
- ownership
Think of tools as an API contract between probabilistic AI behaviour and deterministic business systems.
Phase 5: Add knowledge
Decide whether information should come from:
- direct APIs
- relational databases
- search
- vector retrieval
- knowledge graphs
- document repositories
Do not automatically place every source into a vector database.
Sometimes the best source for a transaction is the system of record itself.
Phase 6: Add human-in-the-loop controls
Human review should be based on risk.
Examples:
No approval: classify a ticket.
Conditional approval: issue a low-value refund.
Mandatory approval: terminate a contract.
Never autonomous: perform a legally or operationally sensitive action without the required human authority.
Phase 7: Evaluate before release
A reliable evaluation suite should include realistic tasks.
Test:
- happy paths
- ambiguous requests
- missing information
- conflicting information
- malicious instructions
- tool failures
- unavailable systems
- unexpected outputs
- edge cases
- escalation behaviour
AWS guidance on evaluating AI agents emphasises that agentic systems require evaluation beyond conventional LLM response quality because they perform dynamic, tool-oriented workflows. AWS guidance on evaluating AI agents
Phase 8: Deploy gradually
A sensible rollout can be:
shadow mode → recommendation mode → approval mode → bounded autonomy → expanded autonomy
This lets the organisation learn where the agent performs reliably before giving it more authority.
09
Security, Governance and Human Oversight
Traditional software security assumes that code behaves predictably.
Agentic systems introduce an additional problem:
The software can make decisions about what to do next.
That changes the security model.
AWS notes that agentic AI systems connect model-based reasoning with tools and APIs that can take actions.
The main risks to design for
Excessive agency
An agent has more permission than it actually needs.
Use least privilege.
An agent that only needs to read CRM records should not have unrestricted write access.
Prompt injection
Untrusted content can contain instructions intended to manipulate an agent.
This is particularly important when agents consume emails, web pages, uploaded files or external documents.
Treat retrieved content as data, not automatically as trusted instructions.
Data leakage
An agent with access to several data sources can potentially combine information that no individual workflow was intended to expose.
Access controls should apply to retrieval as well as actions.
Tool misuse
The risk is not only what the model says.
It is what the tools allow the model to do.
A poorly governed execute_transaction() or delete_customer() tool creates a much larger risk surface than a read-only search tool.
Cascading failures
In a multi-step workflow, one incorrect decision can create downstream actions.
The system needs:
- transaction boundaries
- retries
- circuit breakers
- compensating actions
- approval gates
- clear stop conditions
Governance should be risk-based
NIST's AI Risk Management Framework is designed to help organisations manage AI risks across design, development, deployment, use and evaluation, with trustworthiness considerations integrated throughout the lifecycle. NIST AI Risk Management Framework
For organisations operating in Europe, governance must also be considered against the EU AI Act's risk-based framework. As of August 2026, the European Commission states that the AI Act's governance provisions and several core obligations are in application, while specific high-risk provisions have later transition dates. European Commission — AI Act
The practical takeaway is not to build a compliance checklist after development.
Risk classification should influence architecture before deployment.
10
How to Measure Agentic AI ROI
Agentic AI should not be measured solely by:
- tokens consumed
- number of model calls
- number of agents deployed
- percentage of tasks automated
Those are system metrics.
Business leaders need outcome metrics.
A practical ROI model
Agentic AI value = Benefit created − Total cost of ownership
Benefits might include:
- reduced handling time
- fewer manual steps
- higher resolution rate
- faster response
- more completed transactions
- increased conversion
- lower error rates
- reduced backlog
- reduced cost-to-serve
- improved employee capacity
Costs include:
- model inference
- infrastructure
- integration development
- engineering
- monitoring
- evaluation
- security
- human review
- ongoing maintenance
Example measurement framework
| Metric | Before | After | Business significance |
|---|---|---|---|
| Average handling time | Baseline | Target | Operational efficiency |
| First-contact resolution | Baseline | Target | Customer experience |
| Manual interventions | Baseline | Target | Automation quality |
| Error rate | Baseline | Target | Reliability |
| Escalation rate | Baseline | Target | Autonomy quality |
| Cost per task | Baseline | Target | Unit economics |
| Cycle time | Baseline | Target | Business responsiveness |
| Revenue influenced | Baseline | Target | Commercial impact |
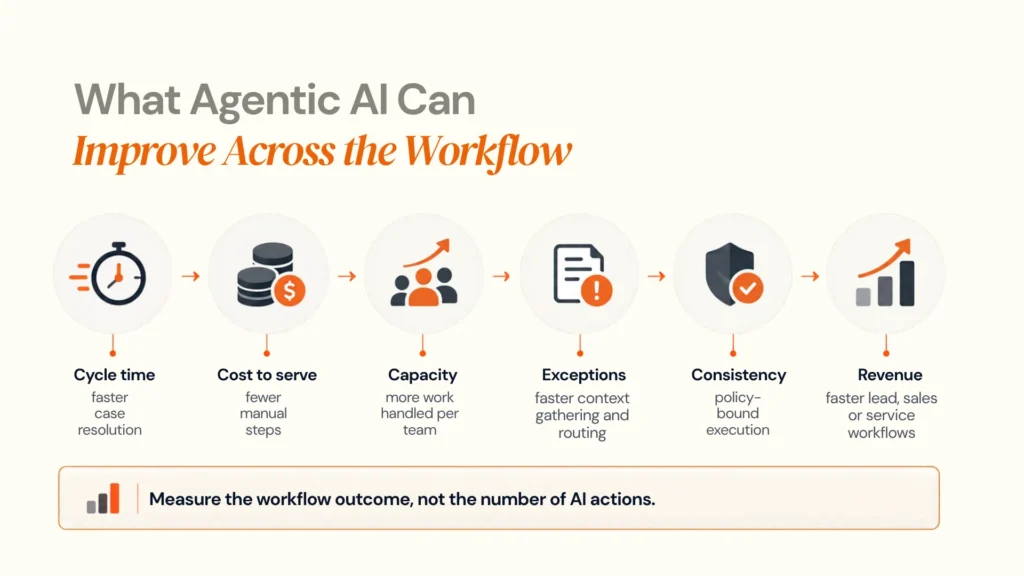
An agent that completes 90% of tasks automatically but creates expensive errors may be a worse business system than one that automates 60% reliably.
Reliability is part of ROI.
11
What Agentic AI Costs
There is no responsible universal price for building an AI agent.
Current 2026 market estimates vary dramatically because vendors use “AI agent” to describe very different systems—from document assistants to multi-system enterprise agents with approval workflows and operational controls.
The more useful approach is to understand the cost drivers.
| Cost driver | Lower complexity | Higher complexity |
|---|---|---|
| Workflow | Single task | Multi-step process |
| Integrations | 1–2 systems | Many enterprise systems |
| AI models | One model | Multiple specialised models |
| Data | One source | Multiple governed sources |
| Retrieval | Basic search | RAG / GraphRAG / knowledge graph |
| Autonomy | Recommendation | Independent execution |
| Security | Standard application controls | Fine-grained agent/tool controls |
| Evaluation | Basic test suite | Continuous behavioural evaluation |
| Deployment | Prototype | Enterprise-scale production |
| Compliance | Low-risk use case | Regulated/high-impact workflow |
For buyers, the most important question is therefore not:
“How much does an AI agent cost?”
It is:
“How much complexity is required to safely automate the workflow that creates the business value?”
This also explains why two vendors can quote dramatically different figures for apparently similar “AI agent” projects.
12
When You Should Not Use Agentic AI
Knowing when not to build an agent is as important as knowing where to use one.
You probably do not need agentic architecture when:
The process is completely deterministic
If the workflow is:
receive form → validate fields → update database → send confirmation
traditional software may be cheaper, faster and easier to test.
There is no meaningful decision-making
Adding an LLM to a deterministic workflow can introduce unnecessary uncertainty.
The volume is too low
A process performed 20 times a year may not justify the engineering and maintenance required for agentic automation.
The data foundation is poor
McKinsey's 2026 research on agentic AI scaling highlights data quality and data architecture as major barriers; the firm's April 2026 research notes that eight in ten companies cite data limitations as a roadblock to scaling agentic AI.
An agent cannot compensate for fundamentally unreliable enterprise data.
The organisation cannot define authority
If nobody can answer:
“What is this agent allowed to do?”
the system is not ready for autonomous execution.
The cost of an error is unacceptable
For some workflows, the correct architecture may be decision support with mandatory human review rather than autonomous execution.
13
What Changes for Technology Buyers
For a CTO or product leader, the arrival of agents changes several procurement questions.
Instead of asking only:
Which model do you use?
Ask:
How does the system evaluate actions?
Instead of:
Can the agent use tools?
Ask:
How are permissions scoped?
Instead of:
Can it operate autonomously?
Ask:
Where does autonomy stop?
Instead of:
Can you build a prototype?
Ask:
How will you operate it at 10,000 or 1,000,000 executions?
Instead of:
What framework do you use?
Ask:
How portable is the architecture if our model, provider or integration strategy changes?
Buying an AI agent is also buying an operating model.
Ask how the vendor handles tool permissions, evaluation, logs, cost controls, failures, model changes and exit scenarios—not only which model is behind the agent.
AI agent vendor evaluation checklist
Question
- What business workflow are we automating?
- What can the agent read?
- What can it write or execute?
- Which actions require approval?
- How are tool calls validated?
- How is behaviour evaluated?
- How is cost monitored?
- How are failures handled?
- Can humans inspect decisions and actions?
- What happens when the model changes?
- How are logs retained?
- What is the rollback strategy?
Why it matters
- Prevents technology-first projects
- Defines data exposure
- Defines operational risk
- Defines autonomy boundaries
- Protects business systems
- Determines reliability
- Protects unit economics
- Determines resilience
- Supports governance
- Reduces vendor/model dependency
- Supports investigation and auditability
- Limits damage from bad actions
14
Agentic AI in 2026: What Has Actually Changed?
The technology is moving quickly enough that organisations need to distinguish genuine platform evolution from marketing language.
Three developments are particularly relevant.
Enterprise adoption is moving from experimentation toward workflow execution
Gartner's 2026 CIO and Technology Executive Survey reported that 17% of organisations had deployed AI agents while more than 60% expected to do so within two years. Gartner's September 2026 analysis of 107 agentic AI deployments argues that the strongest ROI is increasingly associated with specialised, domain-specific agents rather than broad general-purpose autonomy.
McKinsey's April 2026 research provides a different measurement lens: 62% of organisations were experimenting with or piloting AI agents, while 23% reported scaling an agentic AI system somewhere in the enterprise. These figures are not necessarily contradictory because the studies use different populations, definitions and thresholds for deployment versus scaled value.
The shared implication is more useful than either statistic:
Experimentation is advancing faster than reliable enterprise scaling.
Agent infrastructure is becoming more production-oriented
OpenAI's September 2026 Agents API and the July 2026 MCP specification indicate that long-running execution, tool orchestration, context management and interoperability are becoming explicit infrastructure concerns rather than improvised application code.
Governance is moving closer to the engineering layer
AWS, NIST and European regulators increasingly frame AI governance around the complete lifecycle rather than only the model itself. For agentic systems, that means permissions, tools, data, logs, approvals and runtime behaviour become part of the control surface.
15
How Designoweb Can Support an Agentic AI Initiative
Agentic AI projects rarely stop at model integration.
The actual implementation can involve product strategy, workflow discovery, architecture, AI development, backend integration, UX, cloud infrastructure, testing and production operations.
Designoweb's current AI capability includes strategy and advisory, autonomous agents, custom AI solutions, predictive analytics, operational AI and MLOps, alongside full-cycle AI development and enterprise integration.
For teams evaluating the difference between a prototype and a production product, Designoweb's AI development services provide a natural entry point. For broader product delivery, see Designoweb's product development services and our product development process.
Businesses moving from a concept to production can explore AI development services to assess the workflow, architecture and implementation requirements before committing to a particular model or framework.
The broader product layer matters too. Designoweb positions its product development capabilities around scalable digital products, AI applications, integrations and production engineering.
That distinction is important.
An agent that lives inside an existing business platform has different requirements from a new AI-native product.
Relevant Designoweb proof
Designoweb's existing work provides adjacent proof across AI, workflow and product engineering:
- Gold Sky AI-powered hiring case study combines AI-powered candidate matching with recruitment workflows and concierge support.
- VASD AI-powered diagnostics case study combines AI-driven diagnosis, recommendations and service-booking workflows within a digital product.
- Nexlead AI-powered advertising case study connects AI-powered digital advertising with campaign requests, approvals and scheduling across a scalable platform.
These should be understood as examples of AI and connected workflow engineering—not represented as proof that those products themselves are autonomous agentic systems.
16
A Practical Roadmap for Businesses Considering Agentic AI
The safest way to approach agentic AI is to increase autonomy as evidence supports it.
Stage 1 — Identify
Choose one workflow with:
- measurable value
- significant manual effort
- sufficient data
- clear ownership
- manageable risk
Stage 2 — Assist
Let AI analyse, recommend and prepare actions while humans remain responsible for execution.
Stage 3 — Execute with approval
Allow the agent to perform low-risk actions and request human approval for higher-risk actions.
Stage 4 — Automate bounded workflows
Expand autonomy where the agent has demonstrated reliable performance.
Stage 5 — Scale
Introduce:
- stronger evaluation
- better observability
- cost optimisation
- model routing
- agent registries
- governance
- reusable tools
- cross-agent orchestration where justified
The objective is not maximum autonomy.
It is maximum useful autonomy within an acceptable risk boundary.
Final Agentic AI Decision Checklist
Before approving an AI agent initiative, make sure the team can answer these questions clearly:
| Question | What a clear answer looks like |
|---|---|
| What workflow are we changing? | One defined process with a measurable outcome |
| Why does it need agency? | The process contains meaningful variation or multi-step decisions |
| What data does the agent need? | Named systems of record and approved knowledge sources |
| Which tools can it use? | Narrow, typed, permission-controlled interfaces |
| What can it change? | Explicit action boundaries and approval thresholds |
| How will we evaluate it? | Realistic test cases, failure cases and production monitoring |
| What is the business KPI? | Cycle time, resolution, conversion, cost, error rate or another defined outcome |
| What happens when it fails? | Retry, escalate, stop, compensate or rollback |
| How will the architecture scale? | Clear path for volume, integrations, model changes and operating cost |
| Who owns the system? | Named business, product, engineering and governance owners |
Conclusion: The Real Opportunity Is Workflow Transformation
Agentic AI is not valuable because an AI system can “think” more independently.
It is valuable when that capability changes how work gets done.
The strongest business cases tend to sit between two extremes.
At one end, there are deterministic workflows where traditional software remains the better choice.
At the other, there are complex workflows requiring judgement, context, multiple systems and dynamic decisions.
Agentic AI is most useful in the space between them.
The practical path is therefore:
Start with the workflow.
Define the outcome.
Design the authority boundary.
Connect the right tools and data.
Evaluate behaviour.
Measure business impact.
Increase autonomy only when the evidence supports it.
For companies evaluating an agentic AI initiative, the next step should not necessarily be building an agent.
It may be mapping the workflow that the agent is supposed to improve.
That is where a technology partner can create value: turning an attractive AI concept into a production architecture that works with the systems, people, controls and commercial objectives already in the business.
Author
Frequently Asked Questions
01
What is agentic AI?
Agentic AI describes AI systems that can pursue a defined goal through multiple steps by reasoning over context, selecting tools, taking actions and adapting based on results within defined boundaries.
02
Is agentic AI the same as an AI agent?
The terms are closely related but not identical. An AI agent is an individual software component that can perform tasks. Agentic AI generally describes the broader system or approach in which agents use models, tools, data and orchestration to pursue goals.
03
What is the difference between agentic AI and generative AI?
Generative AI primarily creates outputs in response to instructions. Agentic AI extends that capability into multi-step decision-making and action. An agent may use generative AI internally while also interacting with tools, systems and workflows.
04
Are AI agents fully autonomous?
Not necessarily. Production agents are commonly designed with explicit autonomy boundaries, approval checkpoints, permission controls and escalation rules. The appropriate degree of autonomy depends on the risk and value of the workflow.
01
How do you build an AI agent?
A production implementation usually involves defining the workflow and business outcome, designing the agent architecture, selecting models, connecting trusted data, implementing tools, adding permissions and guardrails, building evaluation tests, deploying gradually and monitoring real-world behaviour.
02
Should a company build one AI agent or a multi-agent system?
Start with the simplest architecture that solves the workflow. A single agent or deterministic workflow is often sufficient. Multi-agent designs become more appropriate when the workflow has genuinely separable responsibilities that benefit from specialised agents.
03
What systems can an AI agent integrate with?
Potential integrations include CRM, ERP, databases, customer-support platforms, internal APIs, communication systems, document repositories, analytics systems and specialised business applications. The available integrations depend on the system architecture and the permissions granted to the agent.
01
Does agentic AI require RAG?
No. RAG is useful when an agent needs external knowledge at runtime, but not every agent needs RAG. Some agents can rely on structured APIs, databases, deterministic rules or transactional systems instead.
02
Does an AI agent need memory?
Not always. Short-term state is often useful for multi-step tasks. Long-term memory is appropriate only when persistent context creates real value and the organisation has a clear approach to retention, privacy and access control.
03
Which LLM should an AI agent use?
There is no universally correct model. Selection should consider reasoning capability, tool-use performance, latency, cost, privacy, context requirements, structured output reliability and deployment constraints.
01
How much does AI agent development cost?
There is no meaningful single price. Cost is driven by workflow complexity, number of integrations, model usage, data architecture, security, autonomy level, evaluation requirements, infrastructure and compliance needs. A narrowly scoped internal workflow can be fundamentally different from an enterprise multi-system agent.
02
What is the biggest cost in an AI agent project?
The model API is only one cost component. Integration engineering, data preparation, evaluation, security, observability, infrastructure, human oversight and ongoing maintenance can materially influence total cost of ownership.
01
What are the main risks of agentic AI?
Key risks include excessive permissions, prompt injection, data leakage, incorrect tool use, cascading failures, poor evaluation, unpredictable costs and insufficient auditability.
02
How should AI agents be secured?
Use least-privilege access, explicit tool permissions, input and output controls, data-access policies, approval gates for sensitive actions, audit logs, sandboxing where appropriate and continuous evaluation.
03
Should humans remain in the loop?
For many workflows, yes. Human involvement should reflect risk. Low-risk repetitive activities may be automated, while high-impact or irreversible actions should typically have stronger approval or escalation controls.
01
What should I ask an AI agent development company?
Ask what workflow they are solving, how they define agent authority, how tools and permissions are controlled, how behaviour is evaluated, how costs are monitored, how failures are handled, how the architecture scales and how easily the system can adapt when models or vendors change.
02
How do I know whether my business needs agentic AI?
Start with the workflow rather than the technology. Agentic AI is worth evaluating when the process has measurable value, multiple steps, variable inputs, meaningful decisions, system integrations and enough volume to justify the investment.