
Key Takeaways
01.
A fintech or e-commerce Android app is a business system exposed through a mobile interface.
02.
Financial transactions, orders and inventory need clear sources of truth.
03.
New Android apps and app updates submitted to Google Play from August 31, 2026 must target Android 16 (API 36) or higher. Existing apps need Android 15 (API 35) or higher to remain available to new users on newer Android versions. Google Play target API requirements
04.
Modern Android architecture benefits from clear UI and data layers, repositories, unidirectional data flow and testable state management. Android architecture recommendations
05.
Fintech security and compliance decisions belong in discovery and architecture, not just pre-launch QA.
06.
Payment flows should minimise the amount of sensitive payment data the app and backend directly handle.
07.
E-commerce apps need reliable catalogue, cart, inventory, checkout, payment and order states.
08.
Offline caching can improve UX, but cached financial data must not become the source of truth.
09.
Development cost is driven heavily by backend complexity, integrations, security, compliance and operational tooling—not only by screen count.
10.
A strong development partner should explain failure recovery, reconciliation, security testing, ownership and maintenance.
For a fintech or e-commerce business, the Android app is usually the part customers see. It is rarely the part carrying the hardest engineering decisions.
Behind a balance screen, wallet, product page or checkout button sit APIs, authentication, payment providers, databases, inventory services, fraud controls, analytics, notifications and operational workflows. A polished UI can make those systems feel simple, but it cannot compensate for an architecture that handles money, stock or customer data poorly.
That is why Android app development for fintech and e-commerce has to begin before UI implementation.
The important questions are not only:
What should the app look like?
They are also:
- Which system owns the truth?
- What happens when a payment times out?
- How do retries avoid duplicate transactions?
- Which information can be cached?
- What data should stay off the device?
- How are identity and transaction approvals separated?
- How will the team reconcile financial events?
- Which platform and market requirements apply?
In this guide, we are going to look at the architecture behind production-ready fintech and e-commerce Android apps, when to choose native Android or cross-platform development, which features deserve priority, how payments and security should be engineered, how to plan the development process, what affects the cost and timeline, and how to evaluate an Android app development partner.
01
Why Fintech and E-commerce Android Apps Are Different
The two sectors have different primary jobs.
E-commerce focuses on products, discovery, pricing, stock, carts, orders, delivery and customer experience.
Fintech focuses on accounts, transactions, balances, identity, payments, risk and financial controls.
When one product combines both—for example, commerce with a wallet or instalment payments—a single checkout may involve several domain systems:
| Domain | Source of truth | Typical responsibility |
|---|---|---|
| Customer | Account service | Identity, profile, preferences |
| Commerce | Commerce platform | Catalogue, pricing, carts, orders |
| Inventory | Inventory service | Stock, reservation, warehouse state |
| Payments | Payment service/provider | Authorisation, capture, refund |
| Finance | Ledger/accounting | Debits, credits, balances, reconciliation |
| Risk | Fraud/risk system | Risk signals, velocity, review |
| Notifications | Notification service | Push, email, SMS and transaction events |
The Android app should orchestrate those capabilities rather than becoming the source of truth for business-critical rules.
A product image can be cached.
A recently viewed product can be cached.
A financial balance should still come from an authoritative service when freshness matters.
An order and a financial ledger also should not be treated as the same data model. One represents commerce state; the other represents financial state.
The first architectural rule
Build the mobile experience around authoritative backend systems.
Do not make the Android client responsible for proving that money, inventory or orders are correct.
This becomes especially important with retries. A user can press Pay, lose connectivity and reopen the app. If the backend interprets every retry as a new transaction, a recoverable network problem can become a financial incident.
For appropriate transaction APIs, idempotency is therefore a core design concern—not a later optimisation.
02
When Android Is the Right Platform
Android can be a strong primary platform for products that need wide device coverage, Android-specific capabilities or a large existing Android customer base.
But Android first and Android only are different product strategies.
Native Android
Native Android is usually the strongest fit when the product depends heavily on Android APIs, platform-specific capabilities, specialised SDKs or very fine control over device behaviour.
Google's current architecture guidance recommends clear UI and data layers, repositories, unidirectional data flow and testable state management. Jetpack Compose is the recommended modern toolkit for new Android UI work. Android architecture guidance
Cross-platform
Flutter and React Native can make sense when Android and iOS are both strategic and a shared codebase improves delivery efficiency.
| Approach | Strong fit | Main trade-off |
|---|---|---|
| Native Kotlin + Compose | Android-specific or deeply integrated products | Separate iOS implementation |
| Flutter | Shared Android + iOS product delivery | Some specialised features still need native work |
| React Native | Teams already invested in React/TypeScript | Native modules may still be required |
| Hybrid/WebView | Lightweight companion experiences | Poor fit for highly interactive, high-trust flows |
The question is which architecture gives the product the best balance of capability, speed, maintainability and long-term cost.
A 2026 platform requirement to plan early
From August 31, 2026, Google Play requires new apps and app updates to target Android 16/API 36 or higher. Existing apps need Android 15/API 35 or higher to remain available to new users on newer Android versions. Google Play target API level requirements
03
The Architecture Behind a Production-Ready App
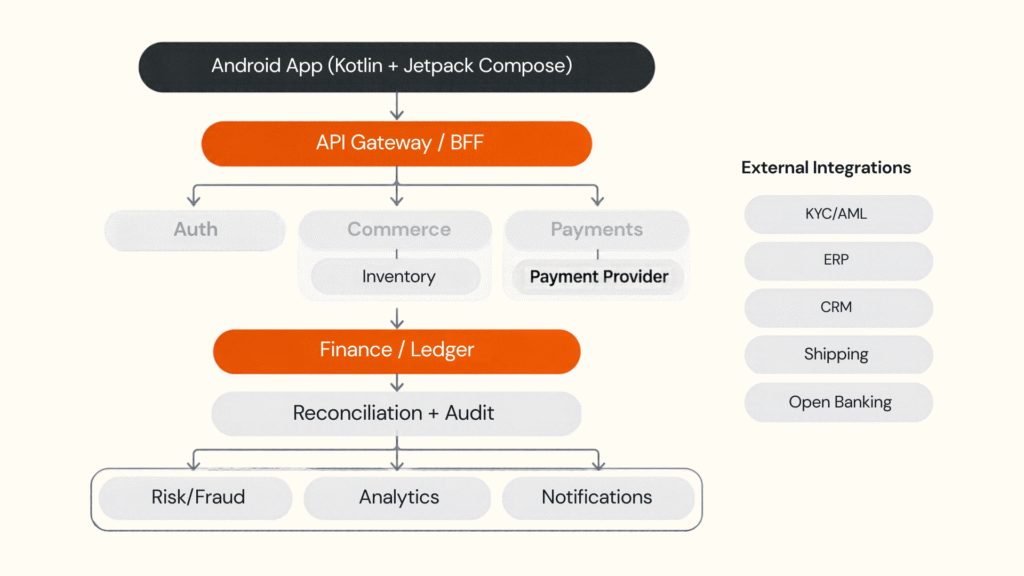
A fintech or e-commerce Android application is usually easier to maintain when responsibilities are separated.
A practical reference architecture is:
Keep the Android layer focused
The mobile client can contain:
- UI
- ViewModels/state holders
- Local persistence
- Repositories
- Session management
- Analytics
- Network handling
Android's guidance explicitly recommends a layered architecture in which the UI consumes application state through repositories and follows unidirectional data flow. Android app architecture
Use a BFF when the product needs aggregation
Separate orders from the financial ledger
Consider a £200 wallet-backed order.
A business system may need to track:
- Order created
- Inventory reserved
- Payment authorised
- Wallet debit recorded
- Order confirmed
- Fulfilment initiated
Each event has a different meaning.
An order database should not become the financial ledger.
Separating commerce state from financial records makes refunds, disputes, chargebacks and reconciliation easier to reason about.
Design for retries and uncertain outcomes
A production payment system should have explicit states such as:
-
1
Initiated
-
2
Pending
-
3
Authorised
-
4
Captured
-
5
Failed
-
6
Refunded
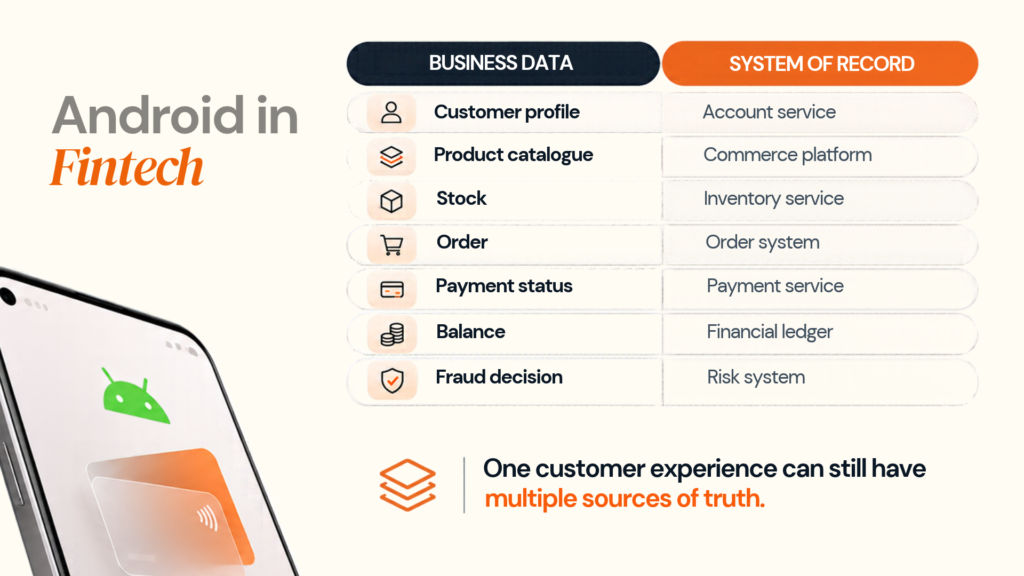
The exact states vary by payment method, but the principle is the same: the user should never have to guess whether money moved.
Offline behaviour needs different rules by domain
Offline support is useful for:
- Product browsing
- Recently viewed items
- Saved content
- Drafts
- Some support workflows
For financial products, a cached display may be helpful, but the app should distinguish between:
Cached information
and
authoritative current state
That distinction protects trust.
Performance and adaptive Android UX
Android's current guidance covers adaptive layouts across phones, tablets and foldables, while performance should be measured on real user journeys. Android adaptive quality guidance
Decide early what loads first, what can be cached or deferred, how the app behaves on slow networks and which devices need explicit testing.
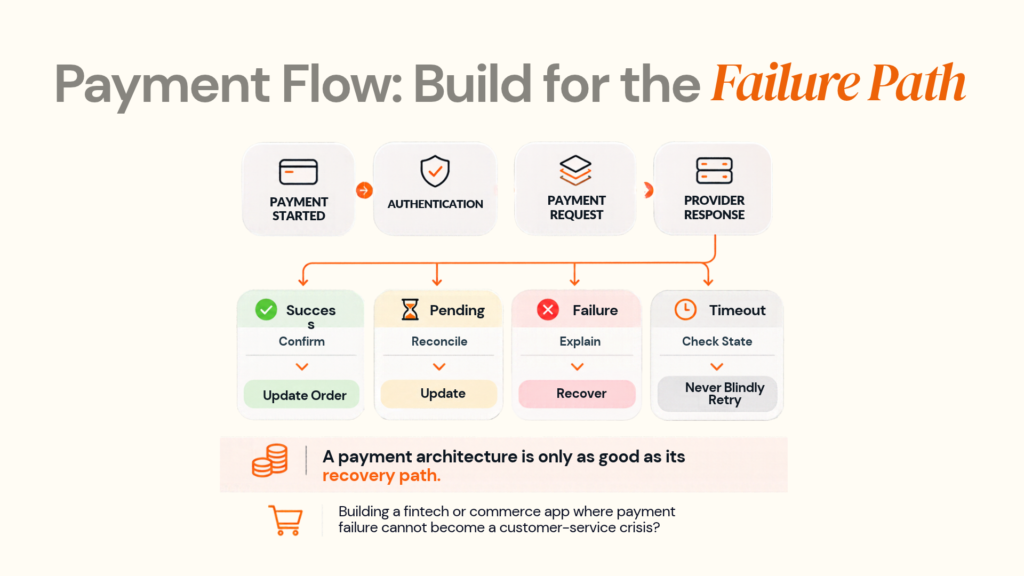
| BUSINESS DATA | SYSTEM OF RECORD |
|---|---|
| Customer profile | Account service |
| Product catalogue | Commerce platform |
| Stock | Inventory service |
| Order | Order system |
| Payment status | Payment service |
| Balance | Financial ledger |
| Fraud decision | Risk system |
One customer experience can still have multiple sources of truth.
04
Features That Actually Matter
Feature selection should follow the business model, not a generic “must-have app features” checklist. Core fintech features
| Feature | Why it matters |
|---|---|
| Secure onboarding | Establishes identity and account security |
| MFA / biometrics | Strengthens account access |
| Account and balance views | Financial visibility |
| Transaction history | Trust and dispute support |
| Money movement | Transfers, payments or withdrawals |
| KYC integration | Identity verification where applicable |
| Risk/AML workflows | Appropriate transaction monitoring |
| Notifications | Confirms important account events |
| Statements | Customer and operational records |
| Support/disputes | Recovery when transactions fail |
| Auditability | Explains what happened and when |
A personal-finance app that aggregates accounts has a different architecture from a wallet that initiates money movement.
Core e-commerce features
| Feature | Why it matters |
|---|---|
| Catalogue | Product discovery |
| Search and filtering | Reduces time to product |
| Variants | Handles real inventory complexity |
| Cart | Preserves purchase intent |
| Checkout | Converts intent into revenue |
| Payment | Completes the transaction |
| Order tracking | Reduces uncertainty |
| Returns/refunds | Supports post-purchase operations |
| Personalisation | Improves discovery when backed by useful data |
| Admin tools | Keeps operations manageable |
Combined fintech + commerce features
Embedded finance can create a much larger product scope:
- Digital wallets
- Instalment payments
- Cashback
- Business credit
- Invoice financing
- Merchant settlement
- Multi-currency support
- Financial dashboards
- Transaction categorisation
Do not put all of them into the first release.
A better MVP proves one customer problem, one transaction journey and one commercial model before expanding the financial surface area.
05
Security, Payments and Compliance
Security should be part of the architecture from the beginning.
OWASP's Mobile Application Security Verification Standard provides a common baseline for secure mobile development, covering areas such as storage, cryptography, authentication, network security, platform interaction, resilience and privacy. OWASP MASVS
OWASP also released the stable MASWE 1.0.0 in August 2026, adding a structured catalogue of mobile security weaknesses alongside MASVS and MASTG. OWASP MASWE 1.0.0
Secure the device layer
Review credential/token handling, encryption, secure network communication, session management, device compromise, sensitive screenshots, rooted environments where relevant, error handling, and logging.
The goal is to reduce the attack surface and limit the impact of compromise.
Separate login from transaction approval
Logging in and approving a high-value payment are not necessarily the same security event.
For sensitive transactions, the system may need stronger authentication, transaction context or step-up verification.
It should be able to answer:
Who authenticated?
What did they approve?
When did they approve it?
What amount or destination was involved?
Keep payment scope under control
For card payments, businesses should reduce the amount of raw payment information their own infrastructure handles wherever practical.
Use appropriately scoped payment-provider SDKs and tokenised payment flows, and have the actual PCI scope reviewed against the implementation.
The PCI Security Standards Council maintains the industry's payment-security standards and supporting resources.
Design failure paths before launch
| Failure | Expected product behaviour |
|---|---|
| Timeout after payment submission | Determine transaction state before retry |
| User presses Pay twice | Idempotency prevents duplicate effects |
| Provider rejects payment | Explain failure and offer recovery |
| App closes after success | Reconcile state on restart |
| Refund completes asynchronously | Backend updates payment and order state |
| Webhook arrives twice | Event processing remains idempotent |
| Inventory disappears | Prevent invalid order completion |
| Session expires | Re-authenticate safely |
Compliance is market-specific
There is no universal fintech compliance checklist.
The applicable perimeter depends on the product, geography, payment model, regulated activities, and third parties.
For businesses processing personal data in the UK, the ICO's current guidance says data protection by design and by default should be built into systems from the design stage and throughout the lifecycle. ICO: Data protection by design and by default
For EU financial entities within DORA's scope, the Digital Operational Resilience Act applies from January 17, 2025 and covers ICT risk, operational resilience and ICT third-party risk. European Commission: DORA
For US products, the applicable requirements can vary by state, product, financial activity and data flow. The software team should translate confirmed legal requirements into technical controls rather than inventing the regulatory perimeter.
06
A Better Android Development Process
The safest way to control cost is to make expensive decisions early.
Phase 1: Product, user and regulatory discovery
Establish:
- Business model
- Target markets
- User roles
- Primary transaction flows
- Data flows
- Third-party systems
- Security requirements
- Compliance perimeter
- Success metrics
- MVP boundaries
The output should be clear enough for engineering to identify major unknowns before sprint planning.
Designoweb's prototyping services can be useful when teams need to validate a high-risk workflow before committing to full development.
Phase 2: Architecture
Define:
- Android architecture
- Backend boundaries
- API contracts
- Database strategy
- Payment architecture
- Authentication
- Authorisation
- Event flows
- Observability
- Environments
- Recovery and backup strategy
Document major decisions so they do not live only in meetings.
Phase 3: UX and product design
Fintech UX must make money movement understandable.
The user should know:
- Current balance
- What a payment will do
- Whether an action succeeded
- Why it failed
- What happens next
E-commerce UX needs the same clarity around price, availability, delivery and returns.
Designoweb's mobile app design services cover user research, customer journeys, wireframes, prototypes and mobile product design.
Phase 4: Development
Build the critical path first.
For e-commerce:
Catalogue → Product → Cart → Checkout → Payment → Order
For fintech:
Onboarding → Verification → Account → Transaction → Confirmation → History
Do not spend early sprints polishing low-risk screens while the core transaction remains unstable.
Phase 5: Integration and QA
Treat third-party systems as production dependencies.
Test payment providers, identity verification, KYC/AML systems, ERP/CRM connections, shipping, notifications, analytics and account-data APIs.
Designoweb's Quality Assurance Services cover mobile, performance, security, usability and automated/manual testing.
Phase 6: Production readiness
Before launch, review:
- Crash reporting
- API monitoring
- Authentication alerts
- Payment reconciliation
- Backups
- Rollback
- Analytics
- Support procedures
- Google Play requirements
- Privacy documentation
A release is ready when the operating team can understand and respond to failures—not merely when the binary installs.
07
Android App Development Cost and Timeline
There is no useful single price for a fintech app or an e-commerce Android app.
Two products may both contain login, search and payments yet have completely different engineering costs because their backend, security, integrations and regulatory requirements differ.
Indicative 2026 planning bands
| Product scope | Planning band | Typical timeline | Main drivers |
|---|---|---|---|
| Proof of concept | 15k–30k | 4–8 weeks | Limited flows, prototype integrations |
| Focused MVP | 40k–80k | 10–16 weeks | Core Android app + backend |
| Production product | 80k–180k | 4–7 months | Security, integrations, operations |
| Complex regulated / marketplace platform | 180k–350k+ | 7–12+ months | Multiple domains, compliance and scale |
These are planning bands derived from the source article's 2026 market framing, not Designoweb prices or fixed quotations. Actual estimates should follow discovery and architecture.
What actually increases cost?
| Cost driver | Why it increases scope |
|---|---|
| Multiple user roles | More permissions and workflows |
| Financial transaction logic | Ledger, reconciliation and recovery |
| KYC/AML | External integrations and verification |
| Payment integrations | Callbacks, failure states and certification needs |
| Marketplace functionality | Sellers, commissions and payouts |
| ERP/CRM integrations | Mapping and synchronisation |
| Security requirements | Threat modelling and testing |
| Native device features | Platform-specific engineering |
| Real-time functions | Messaging, tracking or streaming |
| Offline support | Synchronisation and conflict handling |
| High scale | Performance and observability |
| Compliance | Documentation and control requirements |
A proper proposal should make backend engineering, admin tools, QA, DevOps, security testing, integrations and post-launch support visible.
08
How to Choose an Android Development Partner
Do not choose a fintech or e-commerce development company only from screenshots.
Ask questions that expose engineering maturity.
Ask them to explain the architecture
A strong partner should be able to sketch:
- Android layers
- API boundaries
- Authentication
- Payment flow
- Database ownership
- Integrations
- Monitoring
- Recovery paths
Ask what happens when payment fails
Use a realistic scenario:
“The payment provider succeeds, but the Android app loses connectivity before receiving the response. What does your system do?”
The answer should involve transaction state, reconciliation and safe retries.
It should not be:
“The customer tries again.”
Ask what stays out of the mobile app
Sensitive business rules, secrets, payment credentials and critical authorisation decisions should not be casually pushed into the client.
Ask how security is tested
Look for threat modelling, secure coding, dependency management, mobile/API security testing, penetration testing, logging and incident response.
Ask who owns the product
The contract should clearly cover source code, designs, repositories, infrastructure, app-store accounts, third-party accounts, documentation, credentials and intellectual property.
Ask how maintenance works
Android versions change.
Payment SDKs change.
Cloud services change.
Third-party APIs are deprecated.
09
How Designoweb Can Fit Into the Build
Designoweb's published capabilities cover several parts of the lifecycle relevant to fintech and e-commerce Android products.
Its Android app development services cover end-to-end Android development, API integration, testing, Play Store deployment and ongoing maintenance.
Its mobile app design services cover research, customer journeys, prototyping and product UI.
Its Quality Assurance Services include mobile, performance, security and automated/manual testing.
Its product development services cover product definition, Agile delivery, TDD, DevSecOps and reliability practices.
There are also relevant published projects that demonstrate adjacent capabilities:
- Metaval documents an e-commerce and inventory platform with order tracking and payment-gateway integration.
- VASD demonstrates mobile development across iOS and Android with cloud and machine-learning capabilities.
These projects support the commerce, payment, mobile and cloud/AI capabilities discussed here; they should not be presented as proof of a specific fintech regulatory implementation without separate evidence.
The right starting point
A serious fintech or e-commerce Android project should usually begin with:
Business problem → customer journey → transaction/data flow → MVP → architecture → integrations → security → delivery plan
That gives the business something more useful than a feature list: a product plan that can actually be estimated and operated.
Start With the System Behind the Screen
The strongest fintech and e-commerce Android apps make complicated infrastructure feel simple.
Customers see:
A balance.
A product.
A checkout button.
An order confirmation.
Behind each of those is a set of systems that need to agree about identity, data, money and state.
Build those foundations first.
Then make the Android application the clearest possible expression of them.
Author
Frequently Asked Questions
01
What is Android app development for fintech and e-commerce?
It is the development of Android applications that support financial and commerce workflows such as payments, account management, shopping, checkout, orders, wallets or embedded financial services. The mobile app is one layer of the overall product and normally connects to backend APIs, databases and third-party systems.
02
Can one Android app support both fintech and e-commerce functionality?
Yes. The better approach is to keep the financial and commerce domains logically separated behind clear APIs. For example, an order service should manage order state while a financial ledger manages account transactions. The Android app can present both experiences without making the mobile application the source of truth.
01
Should a fintech app use native Android or Flutter/React Native?
It depends on product requirements. Native Android gives maximum control over platform APIs and Android-specific functionality. Cross-platform frameworks can reduce duplicated development when Android and iOS are both required. For security-sensitive or highly specialised functionality, native modules may still be appropriate even inside a cross-platform product.
02
Is Jetpack Compose suitable for fintech and e-commerce apps?
Yes. Jetpack Compose is Android's recommended modern UI toolkit for new applications and supports adaptive interfaces across different screen sizes and form factors. The broader architecture should still use appropriate separation between UI, data, and business logic.
03
What backend architecture should an Android fintech app use?
There is no mandatory architecture. A modular monolith can work well for an early-stage product, while more distributed architectures may be justified as domains, teams, and transaction volumes grow. The important part is clear ownership of identity, transactions, payments, orders, inventory, and other business domains.
04
How should an Android app handle payment retries?
Use idempotent transaction APIs and explicit payment states. A network timeout should not force the customer to guess whether the payment worked. The backend should be able to determine the transaction state, and the application should reconcile that state when the connection returns.
01
What security standard should be used for an Android fintech app?
OWASP MASVS is a useful mobile security baseline covering storage, cryptography, authentication, network communication, platform interaction, resilience and privacy. It should be combined with backend security controls, organisational controls and any requirements specific to the financial product.
02
Does a fintech Android app need PCI DSS?
It depends on what payment data and payment functions the product handles and how the payment environment is architected. PCI DSS should be assessed based on the actual payment flow and scope rather than assumed solely from the fact that the product accepts payments.
03
Does UK GDPR matter to fintech and e-commerce apps?
Yes, where the product processes personal data within the scope of UK GDPR. The ICO recommends data protection by design and by default, meaning privacy and data protection should be considered during system design and throughout the product lifecycle.
04
Does DORA apply to every fintech application in Europe?
No. DORA applies to financial entities within its defined scope. It addresses ICT risk management and operational resilience, including technology-related third-party risk. The business should determine applicability based on its legal and regulatory position.
01
How much does it cost to build a fintech Android app?
There is no standard price. Current 2026 published estimates range from tens of thousands of dollars for focused products to more than $300,000 for advanced fintech platforms. The biggest variables are product complexity, security, compliance, integrations, financial transaction logic and the development model.
02
How much does it cost to build an e-commerce Android app?
Current published estimates vary significantly depending on whether the product is a simple store, a custom commerce platform, a marketplace or an enterprise system. Published 2026 estimates commonly move from tens of thousands of dollars for basic custom applications to substantially higher budgets for marketplace and enterprise builds.
03
How long does Android fintech app development take?
A focused MVP can take several months, while more complex regulated products can take much longer. The timeline depends on scope, integrations, compliance work, the number of user roles and the degree of custom backend development.
01
What should I ask an Android app development company before hiring them?
Ask how they design transaction flows, handle retries, protect sensitive data, test security, monitor production systems, manage third-party integrations, document architecture and transfer ownership. Ask them to explain one realistic failure scenario rather than relying entirely on portfolio screenshots.
02
Should I build the full product before testing the market?
Usually not. A better approach is to identify the smallest complete customer journey that proves the product's value while preserving the architectural foundations that will be difficult to retrofit later.